TraceX Labs Report Highlights Google Apps Script Abuse for Phishing, Malware and SEO Spam
TraceX Labs Report Highlights Google Apps Script Abuse for Phishing, Malware and SEO Spam TraceX Labs has released a new threat intelligence report examining how Google Apps Script Web Apps can be...

TraceX Labs Report Highlights Google Apps Script Abuse for Phishing, Malware and SEO Spam
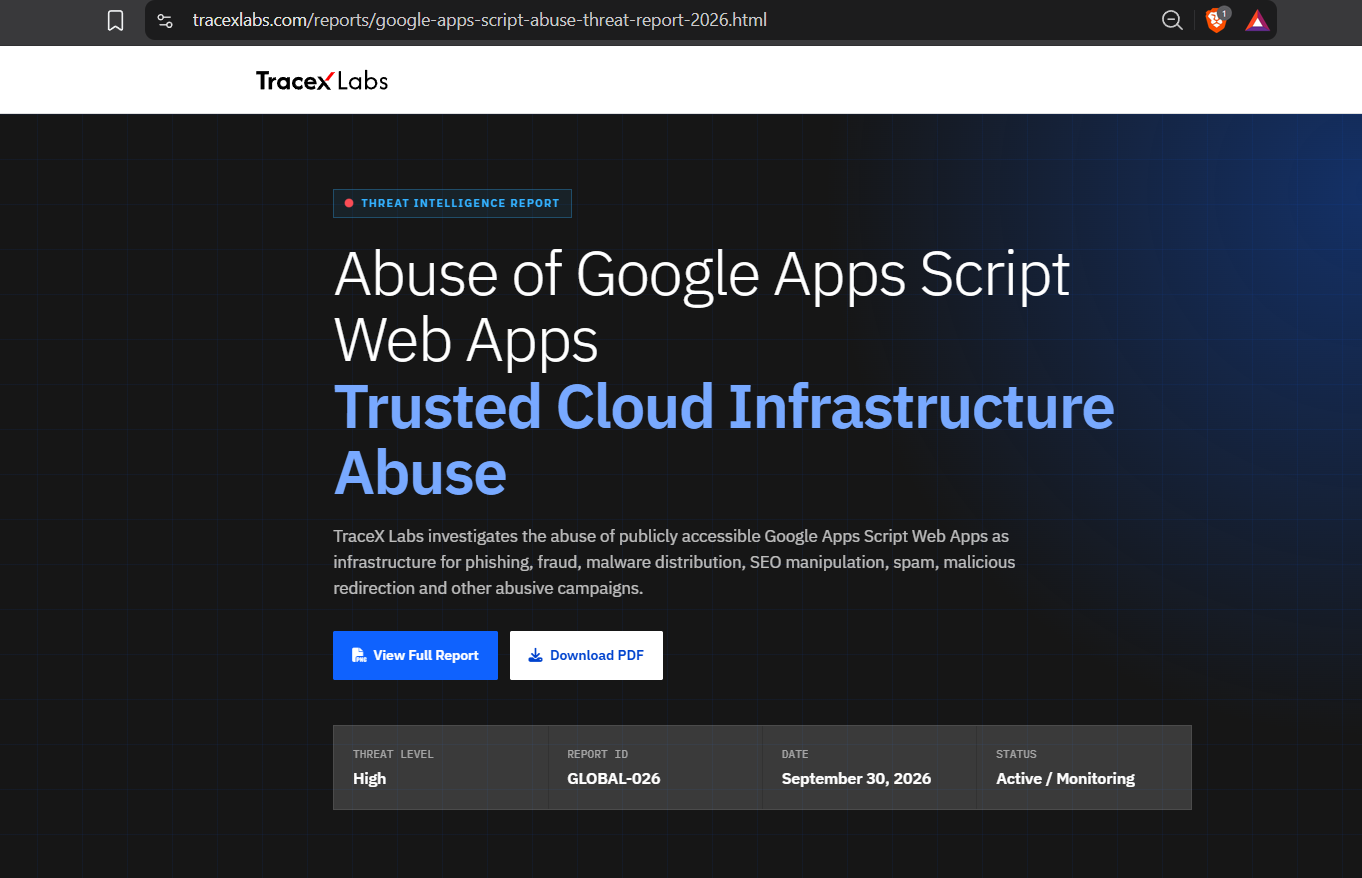
TraceX Labs has released a new threat intelligence report examining how Google Apps Script Web Apps can be abused as part of phishing, fraud, malware distribution, SEO manipulation, spam and malicious redirection campaigns.
The report, published on September 30, 2026, is titled “Abuse of Google Apps Script Web Apps for Phishing, Fraud, Malware Distribution, SEO Manipulation, Spam, CSAM/CSE-Related Abuse and Malicious Redirection.” It is identified as report GLOBAL-026 and carries a high threat assessment.
Google Apps Script used as intermediary infrastructure
Google Apps Script is a legitimate platform used to create web applications and automate workflows across Google services. Its Web Apps can receive requests, generate HTML pages, process parameters and interact with external resources.
TraceX Labs says these capabilities can also be incorporated into abuse infrastructure. In the campaign model described in the report, users may reach an Apps Script URL through search engines, social media, email or messaging services before being directed to another website or resource.
The report makes clear that Google Apps Script itself is not being identified as malicious.
Phishing and financial fraud
The research covers phishing and several forms of online fraud, including credential harvesting, investment scams, employment scams, fake payment activity and social engineering.
According to the report, Apps Script Web Apps can potentially function as landing pages, intermediate pages or redirectors within these campaigns. The final destination and related infrastructure may therefore provide important evidence during an investigation.
TraceX Labs also examined cases involving malicious Android APK distribution and malware delivery. The report recommends supporting malware claims with technical analysis or reliable reputation data rather than relying solely on the presence of an Apps Script URL.
SEO manipulation and search spam
SEO abuse is another major category covered in the report.
TraceX Labs identifies keyword-heavy pages, doorway pages, automatically generated content, repeated templates, large numbers of outbound links and redirect chains as indicators that may warrant investigation.
The report notes that when infrastructure is deliberately used to manipulate search visibility, the activity can potentially map to MITRE ATT&CK technique T1608.006, SEO Poisoning.
The research recommends looking at the behaviour of the infrastructure and its relationship with other campaign components instead of blocking Apps Script solely because it is being used in a suspicious context.
Spam, gambling and synthetic media
The report also examines several other categories of abuse, including gambling and betting spam, adult and NSFW spam, drug-related spam, deepfake and synthetic-media spam, Google video and search spam, and movie-piracy-related search activity.
TraceX Labs notes that the appearance of keywords related to drugs, gambling or piracy does not by itself establish cybercrime. Investigators need additional context and supporting evidence before making a classification.
Suspected CSAM/CSE-related abuse
The report includes a separate section concerning suspected CSAM/CSE-related infrastructure.
TraceX Labs classifies this finding as “Suspected / Corroboration Required”, meaning that the available evidence is not presented as conclusive. The report calls for heightened evidence handling and additional corroboration in such cases.
It also advises researchers and investigators not to unnecessarily download, reproduce or redistribute suspected illegal material. Public reporting should use redacted evidence where appropriate.
A Google URL is not proof that a page is safe
One of the report’s central findings is that the reputation of a cloud provider cannot be used as the only basis for determining whether a particular resource is legitimate.
TraceX Labs states that a Google-owned URL does not establish that Google created or endorsed the content, operates the final destination or has any relationship with external infrastructure linked from the page. The use of HTTPS also does not prove that the content is legitimate.
Detection and threat hunting
For security teams, the report recommends examining Apps Script URLs together with surrounding infrastructure.
Investigators can look for unusual URL parameters, repeated deployment identifiers, suspicious destinations and known malicious infrastructure. Web proxy logs can provide information about redirect chains, downloaded files and final destinations.
Endpoint telemetry can add evidence through indicators such as unexpected APK downloads, suspicious file execution, browser-originated downloads and credential-submission activity.
TraceX Labs recommends correlating the Apps Script URL with destination domains, IP addresses, ASNs, certificates, URL parameters, file hashes and related campaign infrastructure.
Report calls for evidence-based classification
The report uses classifications including Observed, Correlated, Suspected, Potential, Benign and Unknown.
It also cautions that an individual URL, screenshot or piece of infrastructure does not automatically establish attribution, criminal intent, ownership or affiliation with Google.
TraceX Labs recommends an investigation process based on:
Discover → Validate → Correlate → Classify → Report
The report concludes that security teams should focus on behaviour, content, destinations and relationships between infrastructure rather than treating the hosting provider itself as evidence of maliciousness.
The complete TraceX Labs report provides further technical details, detection guidance, investigation procedures and reporting recommendations for security researchers, SOC teams, CERTs and law enforcement.
Report : https://tracexlabs.com/reports/google-apps-script-abuse-threat-report-2026.html