Google Apps Script Abuse: Phishing, Fraud, Malware and CSAM Risks Identified in TraceX Labs Report
TraceX Labs has published a new threat intelligence report examining how Google Apps Script Web Apps may be abused in phishing, fraud, malware distribution, SEO manipulation, spam, malicious...

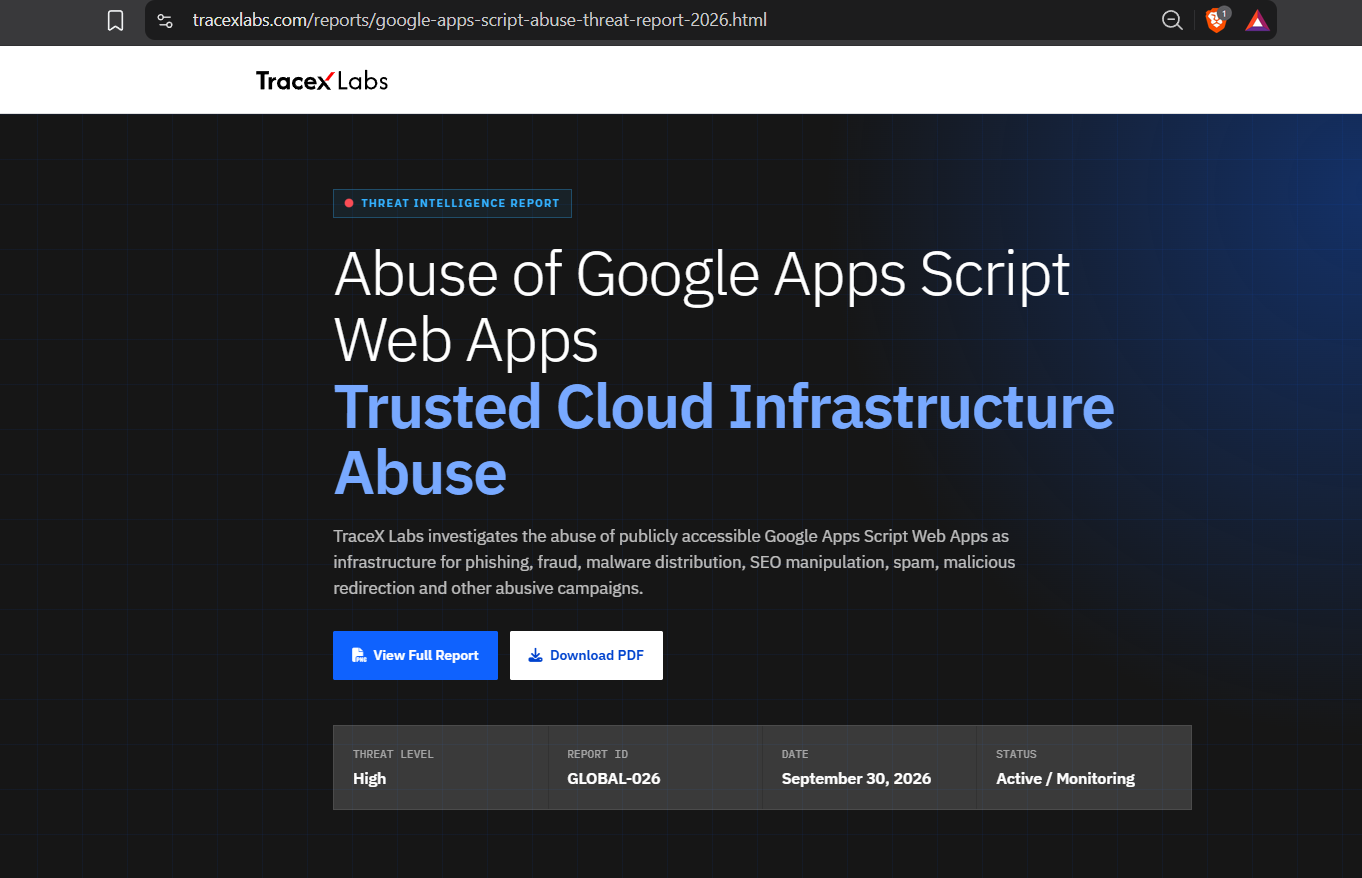
TraceX Labs has published a new threat intelligence report examining how Google Apps Script Web Apps may be abused in phishing, fraud, malware distribution, SEO manipulation, spam, malicious redirection and suspected CSAM/CSE-related activity.
The report, designated GLOBAL-026 and dated September 30, 2026, carries a High threat assessment with an Active / Monitoring status. It investigates how publicly accessible Google Apps Script Web Apps can potentially become components of broader campaigns involving malicious or abusive content.
Google Apps Script Abuse Examined by TraceX Labs
TraceX Labs emphasizes that Google Apps Script is a legitimate platform widely used for software development, automation, education, data processing and Google Workspace workflows. The report focuses on the third-party abuse of legitimate infrastructure, rather than suggesting that malicious functionality is inherent to Google Apps Script itself.
According to the report, Apps Script Web Apps can process HTTP requests, generate HTML, handle URL parameters, interact with external resources and participate in redirect workflows. These capabilities can potentially allow an Apps Script URL to function as one element within a larger attack or abuse chain.
A campaign may initially reach users through search engines, social media, email or messaging platforms before directing them to an Apps Script URL. The Apps Script endpoint may then display a landing page, operate as a dynamic application or redirect the visitor toward external infrastructure.
Phishing, Fraud and Malware Distribution
The investigation covers several forms of abuse, including phishing, credential harvesting, malicious APK distribution, malware delivery, malicious redirects and social engineering.
TraceX Labs also examines indicators associated with investment scams, employment scams, fake payment pages, UPI-related fraud, cryptocurrency-related fraud and impersonation campaigns.
During its investigation, TraceX Labs documented Apps Script-associated infrastructure connected with APK downloads, malware-related landing pages and redirects toward suspicious payload infrastructure. The report classifies relevant evidence using categories such as Observed / Correlated, rather than treating every Apps Script deployment as malicious.
The investigation also identifies indicators associated with suspected investment and employment scams, including payment requests, requests for personal information, unrealistic salary claims and external messaging-platform contacts.
SEO Manipulation and Spam
Search-engine manipulation represents another significant area examined by the report.
TraceX Labs identifies potential indicators such as keyword-heavy landing pages, doorway pages, automatically generated content, large numbers of outbound links, repeated page templates, redirect chains, affiliate links and campaign-specific URLs.
Where search visibility is deliberately manipulated to expose users to malicious or unwanted content, the report notes a potential connection to MITRE ATT&CK T1608.006 — Stage Capabilities: SEO Poisoning.
The investigation also examines Google search and video spam as well as movie-piracy-related search infrastructure. According to the report, these ecosystems can potentially include advertising networks, redirects, malvertising and malware-delivery infrastructure.
Gambling, Adult Spam and Synthetic Media
The report also investigates additional abuse categories, including gambling and betting spam, adult/NSFW spam, drug-related search spam and deepfake or synthetic-media-related spam.
TraceX Labs documented infrastructure containing gambling-related keywords, casino promotions, affiliate links and redirects. Some investigated campaigns combined adult-content and gambling-related material.
The report also examines deepfake and synthetic-media activity, including manipulated-media claims, fake celebrity content, synthetic-media services and external distribution platforms.
TraceX Labs cautions that the appearance of an individual keyword or category alone does not automatically establish illegal or malicious activity. Classification requires consideration of the broader context, destination infrastructure and supporting evidence.
Suspected CSAM and Child Exploitation Infrastructure
A separate section of the report addresses suspected CSAM/CSE-related infrastructure.
TraceX Labs classifies this evidence as “Suspected / Corroboration Required” and treats the category as requiring enhanced evidence handling.
The report recommends that investigators avoid unnecessarily downloading, reproducing or redistributing underlying material. Public reporting should contain only appropriately redacted evidence where necessary.
The investigation also treats NCII and sextortion as separate sensitive investigative categories. Their inclusion represents potential impact or investigation classifications and does not mean that every Apps Script deployment examined by TraceX Labs is connected to these activities.
A Google Domain Does Not Guarantee a Safe Destination
One of the report’s central observations is that a URL hosted on a Google-owned domain should not automatically be considered trustworthy solely because it uses Google’s infrastructure.
TraceX Labs notes that a Google-hosted URL does not, by itself, establish that Google created or endorsed the content, operates the final destination or that associated external infrastructure is trustworthy.
The report also emphasizes that HTTPS provides encrypted communication but does not independently establish that a website, file or destination is legitimate.
What Security Teams Should Monitor
TraceX Labs recommends monitoring Apps Script URLs based on their behaviour and surrounding infrastructure, rather than broadly blocking Google services.
Relevant indicators include:
- Suspicious Apps Script URLs
- Repeated deployment IDs
- Unusual URL parameters
- Redirect chains
- Known malicious destinations
- Downloaded APKs or suspicious files
- Credential-submission forms
- Unusual browser behaviour
- Suspicious endpoint activity
The report recommends correlating Apps Script URLs with associated destination domains, IP addresses, ASNs, certificates, URL parameters, file hashes and related infrastructure.
Using multiple independent indicators can help security teams distinguish legitimate applications from potentially abusive deployments and prioritize investigations.
TraceX Labs Calls for Behavioural Analysis
The report identifies several challenges that can complicate investigations, including the extensive legitimate use of Google Apps Script, changing search-engine indexing, infrastructure that disappears quickly, redirects that may vary according to user-agent or geographic location, and potential false positives generated by reputation services.
To address these limitations, TraceX Labs recommends classifications such as Observed, Correlated, Suspected, Potential, Benign and Unknown.
The objective is to prevent technical capabilities or isolated indicators from being incorrectly presented as confirmed malicious activity.
In its final assessment, TraceX Labs describes trusted cloud infrastructure abuse as an important challenge for threat intelligence and defensive detection. The report identifies potential relationships between Apps Script infrastructure and campaigns involving phishing, fraud, malware distribution, SEO poisoning, spam, malicious redirection, NCII, sextortion and suspected CSE/CSAM-related activity.
The recommended investigative model is:
Discover → Validate → Correlate → Classify → Report
Under this approach, investigators consider behaviour, content, destination infrastructure and campaign relationships alongside the reputation of the hosting provider.
TraceX Labs GLOBAL-026 Report
The complete GLOBAL-026 Threat Intelligence Report is available from TraceX Labs:
https://tracexlabs.com/reports/google-apps-script-abuse-threat-report-2026.html